OpenOSINT
AI-powered OSINT agent with interactive REPL, MCP server, and CLI. 20 tools. Works with Claude, GPT-4, or local models. For authorized security research only.
Safety scan
A static text scan, not a guarantee. Select the badge to see what was scanned and every finding.
Check it deeper on your machine
It has changed since its scan on 11 Nov 2026.
As a Claude Code plugin, install it and then ask Claude Code:
/plugin marketplace add keithmackay/mackayi/plugin install scanskillsafety@mackayiDo a deep scan of https://github.com/OpenOSINT/OpenOSINT with scanskillsafety
Or from a terminal, clone it and run it:
git clone https://github.com/keithmackay/scanskillsafety-skill ~/.claude/skills/scanskillsafetynode ~/.claude/skills/scanskillsafety/cli.cjs --deep 'https://github.com/OpenOSINT/OpenOSINT'
It checks the exact commit: every file, its packages against OSV (api.osv.dev), how it compares with this page's scan (findsafeskills.com receives the repository's address), and, if you agree, Claude reading every file with your own Claude subscription. It never runs the code.
Badge for your README

Markdown
[](/listings/openosint--openosint)HTML
<a href="/listings/openosint--openosint"><img src="/api/listings/openosint--openosint/badge.svg" alt="findsafeskills safety rating" /></a>Install
Install instructions from the README
As written by the repo's author. findsafeskills has not verified these steps.
Needs [`uv`](https://docs.astral.sh/uv/). No API keys for the default flow.
**Claude Code plugin** (skills plus a passive MCP server):
/plugin marketplace add OpenOSINT/OpenOSINT
/plugin install openosint@openosint
/openosint:osint example.com
**Any agent** (Codex, Gemini CLI, Cursor and other Agent Skills clients):
npx skills add OpenOSINT/OpenOSINT
**MCP server or pip** ([other clients](https://openosint.tech/docs/mcp/)):
claude mcp add openosint -- uvx --from openosint openosint-mcp
pip install openosint && openosint exposure example.com
What was scanned
The files the safety scan read, as written by the repository's author and shown as plain text. Lines with a finding are marked.
.claude-plugin/marketplace.json · Manifest · 15 lines
View this file on GitHub (read at the repository's current version: the scan did not record which commit it read)
This file has changed since it was scanned, so this is not exactly the text that was scanned, and no line is marked. The findings are listed with the safety scan above.
- {
- "name": "openosint",
- "owner": {
- "name": "OpenOSINT",
- "url": "https://github.com/OpenOSINT"
- },
- "description": "OpenOSINT: passive OSINT and exposure checks for Claude Code.",
- "plugins": [
- {
- "name": "openosint",
- "source": "./",
- "description": "Skills /osint and /exposure plus the OpenOSINT MCP server (passive by default, no API keys needed)."
- }
- ]
- }
README.md · README · 186 lines
View this file on GitHub (read at the repository's current version: the scan did not record which commit it read)
This file has changed since it was scanned, so this is not exactly the text that was scanned, and no line is marked. The findings are listed with the safety scan above.
- <!-- mcp-name: io.github.OpenOSINT/openosint -->
- <div align="center">
- <img src="https://raw.githubusercontent.com/OpenOSINT/OpenOSINT/main/docs/assets/logo.svg" alt="OpenOSINT" width="270">
- <p><strong>OpenOSINT is an open-source OSINT agent for investigators and security researchers: 21 public-source tools behind a natural-language interface, with an MCP server.</strong></p>
- </div>
- <div align="center">
- [](https://github.com/OpenOSINT/OpenOSINT/releases)
- [](https://pypi.org/project/openosint/)
- [](LICENSE)
- [](https://registry.modelcontextprotocol.io/servers/io.github.OpenOSINT/openosint)
- [](https://www.ip2location.io/?utm_source=openosint&utm_medium=readme&utm_campaign=ip2location)
- [](https://www.testmuai.com/?utm_source=openosint&utm_medium=opensourcecollab)
- <img src="https://raw.githubusercontent.com/OpenOSINT/OpenOSINT/main/docs/assets/demo-chat.gif" width="720" alt="OpenOSINT answering a question about a company in chat: tool calls with their times, then an answer with a source on every claim">
- **Run it yourself:** `uvx openosint web` (one command, no keys)<br>
- **No terminal?** Use [OpenOSINT Cloud](https://app.openosint.tech/?utm_source=github&utm_medium=readme&utm_campaign=hero) in your browser, first check free
- [Docs](https://openosint.tech/docs/) · [Claude Code plugin](#use-it-from-claude-code-or-any-mcp-client) · [MCP server](https://openosint.tech/docs/mcp/)
- </div>
- ## Quickstart
- Needs [`uv`](https://docs.astral.sh/uv/). No API keys for these commands.
- ```bash
- # Local web app with chat, graph and globe
- uvx openosint web
- # Or one direct check, no AI involved
- uvx openosint exposure example.com
- ```
- ```text
- Grade: B Score: 88/100
- Checks: email OK, registration OK (passive)
- tls OK, http_headers OK (these touch the target)
- [LOW] DMARC has no aggregate report address (dmarc_no_rua)
- [LOW] Strict-Transport-Security header missing (hsts_missing)
- ```
- Real output, trimmed and re-wrapped. More commands: [CLI reference](https://openosint.tech/docs/cli/) · [install guide](https://openosint.tech/docs/install/).
- ## What you can do
- Moved to [Quickstart](#quickstart) above and the [CLI reference](https://openosint.tech/docs/cli/).
- ## Tools
- What it can look up. Per-tool docs: [openosint.tech/tools](https://openosint.tech/tools/). Only passive tools are on by default.
- | Tool | What it finds | Key needed |
- |---|---|---|
- | [`search_dns`](https://openosint.tech/tools/#search_dns) | DNS records, SPF, DMARC | No |
- | [`search_rdap`](https://openosint.tech/tools/#search_rdap) | Registrar, dates, name servers (RDAP) | No |
- | [`search_whois`](https://openosint.tech/tools/#search_whois) | WHOIS registration data | No |
- | [`search_ip`](https://openosint.tech/tools/#search_ip) | Hostname, ASN, city for an IP | Optional |
- | [`search_ip2location`](https://openosint.tech/tools/#search_ip2location) | Geolocation, ISP, proxy/VPN/Tor flags *(sponsored)* | Yes |
- | [`search_gdelt_geo`](https://openosint.tech/tools/#search_gdelt_geo) | Geolocated news mentions (GDELT) | No |
- | [`generate_dorks`](https://openosint.tech/tools/#generate_dorks) | Search-dork URLs for a target | No |
- | [`search_paste`](https://openosint.tech/tools/#search_paste) | Paste-site mentions | No |
- | [`search_github`](https://openosint.tech/tools/#search_github) | Repos, code and users | Optional |
- | [`search_breach`](https://openosint.tech/tools/#search_breach) | Breaches for an email (HaveIBeenPwned) | Yes |
- | [`search_shodan`](https://openosint.tech/tools/#search_shodan) | Open ports and banners | Yes |
- | [`search_censys`](https://openosint.tech/tools/#search_censys) | Hosts and certificates | Yes |
- | [`search_virustotal`](https://openosint.tech/tools/#search_virustotal) | URL, domain and IP reputation | Yes |
- | [`search_abuseipdb`](https://openosint.tech/tools/#search_abuseipdb) | IP abuse reports | Yes |
- | [`search_dorks_live`](https://openosint.tech/tools/#search_dorks_live) | Live dork results via [Bright Data SERP API](https://get.brightdata.com/jx2wfi?sid1=readme&sid2=setup&sid3=search_dorks_live&utm_source=openosint&utm_medium=readme&utm_campaign=setup&utm_content=search_dorks_live)¹ | Yes |
- | [`search_footprint`](https://openosint.tech/tools/#search_footprint) | Web footprint via [Bright Data SERP API](https://get.brightdata.com/jx2wfi?sid1=readme&sid2=setup&sid3=search_footprint&utm_source=openosint&utm_medium=readme&utm_campaign=setup&utm_content=search_footprint)¹ | Yes |
- | [`scrape_url`](https://openosint.tech/tools/#scrape_url) | Page content via [Bright Data Web Unlocker](https://get.brightdata.com/openosint-unlocker?sid1=readme&sid2=setup&sid3=scrape_url&utm_source=openosint&utm_medium=readme&utm_campaign=setup&utm_content=scrape_url)¹ (touches target) | Yes |
- | [`search_username`](https://openosint.tech/tools/#search_username) | Username across platforms (sherlock; noisy) | No |
- | [`search_email`](https://openosint.tech/tools/#search_email) | Accounts tied to an email (holehe; noisy) | No |
- | [`search_domain`](https://openosint.tech/tools/#search_domain) | Subdomains (sublist3r; noisy) | No |
- | [`search_phone`](https://openosint.tech/tools/#search_phone) | Carrier and country (phoneinfoga; unverified) | No |
- Sherlock, holehe, sublist3r and phoneinfoga run as local binaries you install yourself. Setting up the Bright Data tools: [Using OpenOSINT with Bright Data](https://openosint.tech/docs/bright-data/).
- ## Why OpenOSINT
- Tools run as real Python code and every finding cites the call that produced it. Compared with SpiderFoot, OpenOSINT has far fewer modules and is built to be driven by an agent. See the [comparison](https://openosint.tech/docs/#compared-with-other-tools).
- ## Passive by default
- Agents and MCP clients are only offered tools that query third-party sources or compute locally. Anything that touches the target or sends many requests from your IP is off until you opt in (`--allow-active`) and is not listed in an MCP client's `tools/list`. Passive is not private: every service you query sees the query. Details: [Safety](https://openosint.tech/docs/safety/).
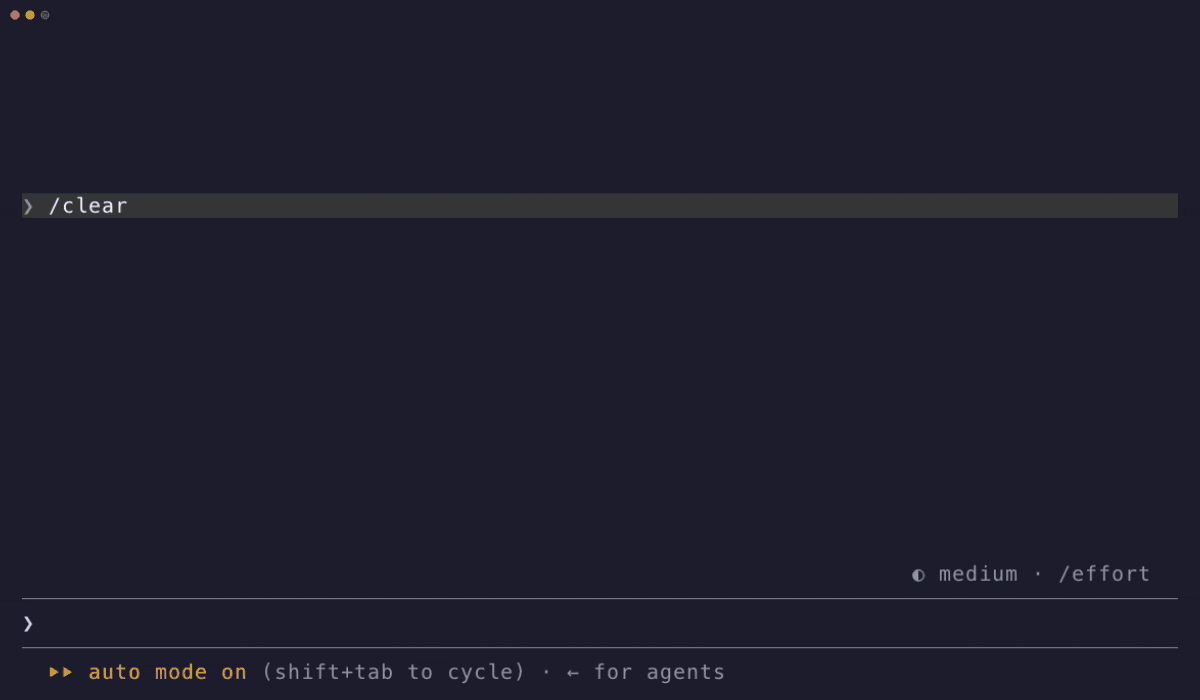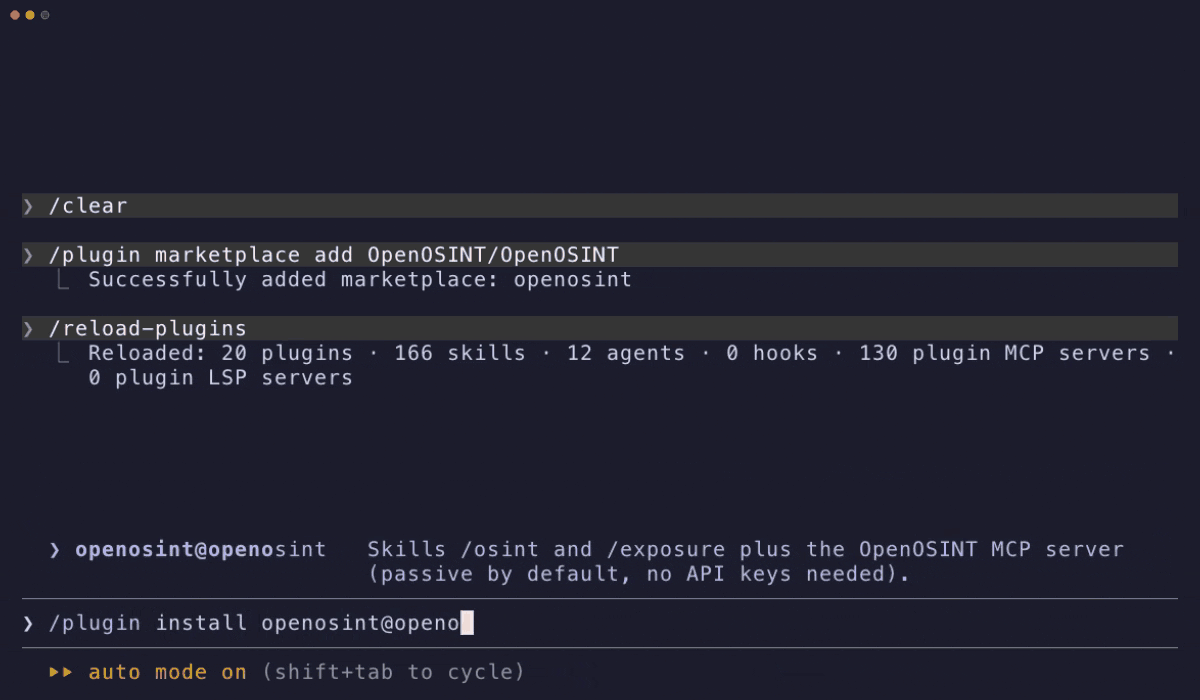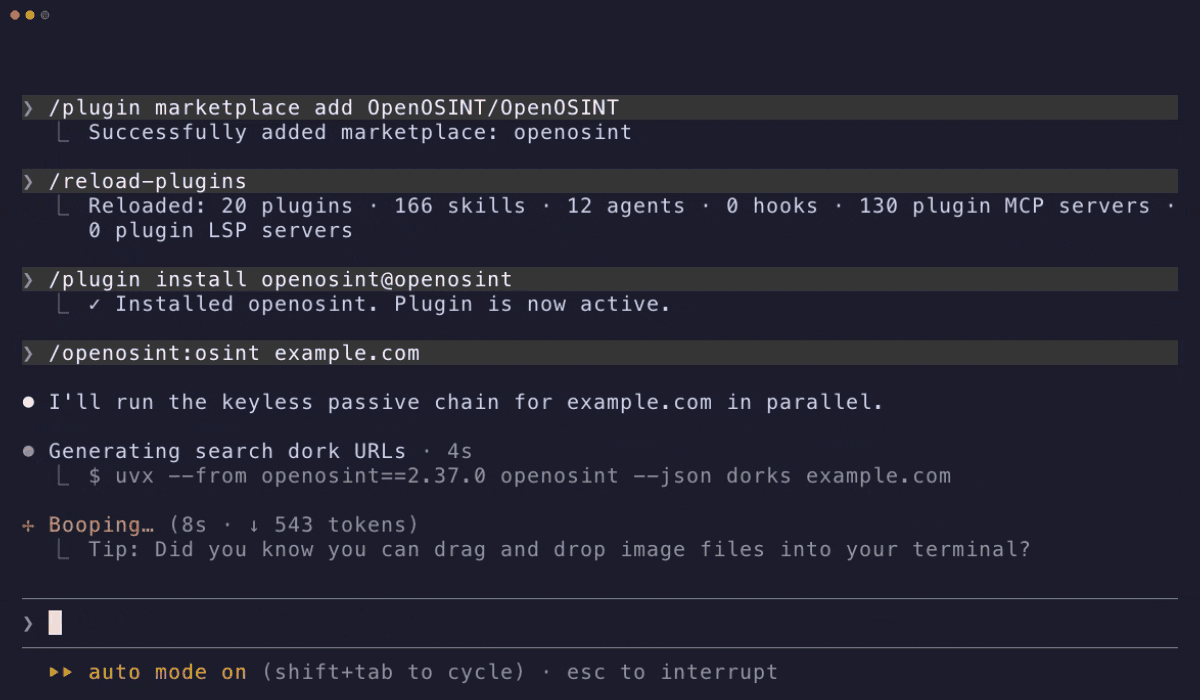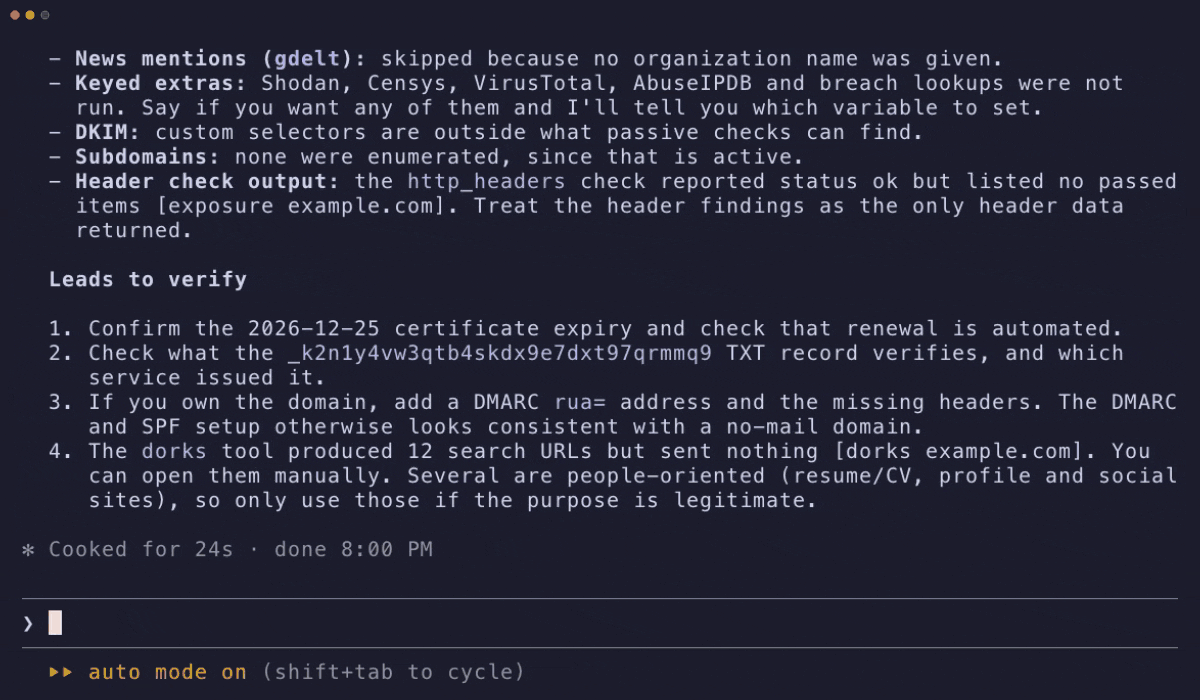
- ## Use it from Claude Code or any MCP client
- ```text
- /plugin marketplace add OpenOSINT/OpenOSINT
- /plugin install openosint@openosint
- /openosint:osint example.com
- ```
- ```bash
- claude mcp add openosint -- uvx --from openosint openosint-mcp
- # Codex, Gemini CLI, Cursor and other Agent Skills clients
- npx skills add OpenOSINT/OpenOSINT
- ```
- 
- Other clients: [MCP docs](https://openosint.tech/docs/mcp/) · [Agent Skill](https://openosint.tech/docs/agent-skill/).
- ## Go deeper
- - **Web UI:** `openosint web`, streaming chat, a news globe and a graph view. [Docs](https://openosint.tech/docs/web-ui/)
- - **REPL:** `openosint` with no arguments. [CLI reference](https://openosint.tech/docs/cli/)
- - **MCP server:** `uvx --from openosint openosint-mcp`. [Client configs](https://openosint.tech/docs/mcp/)
- ### Web UI + globe
- An agent investigation lands as a point on a 3D globe; click it to pivot. [Docs](https://openosint.tech/docs/web-ui/)
- ### Entity graph
- A FollowTheMoney graph with statement-level provenance and a review queue for `same_as` candidates. [Docs](https://openosint.tech/docs/entity-graph/)
- ### External exposure report (beta)
- `openosint exposure example.com` grades email authentication, TLS, registration and security headers A to F. [Docs](https://openosint.tech/docs/exposure/)
- ### Installation
- `pip install openosint` or `uvx openosint web`. Python 3.10+. [Install guide](https://openosint.tech/docs/install/)
- ### MCP Server
- Works in Claude Desktop, Claude Code, Cursor and any MCP client. [Client configs](https://openosint.tech/docs/mcp/)
- ### Configuration
- Keys go in the web UI Settings, `~/.openosint/config.env` or the environment. [All variables](https://openosint.tech/docs/configuration/) · [CLI reference](https://openosint.tech/docs/cli/)
- ### Docker
- `docker compose up --build`, then open <http://localhost:8080>. [Docker notes](https://openosint.tech/docs/web-ui/#docker)
- ## OpenOSINT Cloud
- The same engine as a hosted chat for a domain, an IP address or a company, with a source on every claim. [First check free, no account](https://app.openosint.tech/?utm_source=github&utm_medium=readme&utm_campaign=cloud). Hosted REST and MCP API by request: [commercial@openosint.tech](mailto:commercial@openosint.tech).
- ## Sponsors
- <!-- SPONSORS:START -->
- ### Featured Integrations
- <a href="https://www.ip2location.io/?utm_source=openosint&utm_medium=readme&utm_campaign=ip2location" rel="noopener sponsored"><img src="https://raw.githubusercontent.com/OpenOSINT/OpenOSINT/main/assets/sponsors/ip2location-logo.png" alt="IP2Location.io logo" height="40"></a>
- **[IP2Location.io](https://www.ip2location.io/?utm_source=openosint&utm_medium=readme&utm_campaign=ip2location)** — powers `search_ip2location` · [Integration guide](docs/integrations/ip2location.md)
- > Enhanced IP geolocation, ISP, VPN/Proxy/Tor, and datacenter detection
- <a href="https://www.testmuai.com/?utm_source=openosint&utm_medium=opensourcecollab" rel="noopener sponsored"><picture><source media="(prefers-color-scheme: dark)" srcset="https://raw.githubusercontent.com/OpenOSINT/OpenOSINT/main/assets/sponsors/testmu-ai-white.svg"><img src="https://raw.githubusercontent.com/OpenOSINT/OpenOSINT/main/assets/sponsors/testmu-ai.svg" alt="TestMu AI logo" width="353"></picture></a>
- **[TestMu AI](https://www.testmuai.com/?utm_source=openosint&utm_medium=opensourcecollab)**
- > TestMu AI (formerly LambdaTest) is an AI-native testing cloud platform built for modern engineering teams. It covers everything from autonomous test creation and fast execution to testing AI agents, chatbots and voice assistants.
- _Open: Breach / Compromised-Credential Data · Email / Identity Lookup · Residential Proxies — see [SPONSORSHIP.md](SPONSORSHIP.md)._
- <!-- SPONSORS:END -->
- Sponsor on [Open Collective](https://opencollective.com/openosint_oss) · tiers in [SPONSORSHIP.md](SPONSORSHIP.md) · commercial license and support: [COMMERCIAL.md](./COMMERCIAL.md).
- ## Contributing
- Issues and pull requests are welcome. See [CONTRIBUTING.md](CONTRIBUTING.md). Maintainer: [Tommaso Bertocchi](https://x.com/SonoTommy_) · [@openosint_oss](https://x.com/openosint_oss). Contributors: [@consocio](https://github.com/consocio) ([#6](https://github.com/OpenOSINT/OpenOSINT/pull/6)).
- ## Legal Disclaimer
- For authorized security research and educational use only. Only investigate targets you own or are permitted to assess. Passive does not mean anonymous. Full text: [DISCLAIMER.md](DISCLAIMER.md).
- ## License
- MIT. See [LICENSE](./LICENSE).
- ¹ Bright Data links in this README are affiliate/referral links: OpenOSINT earns a commission if you sign up through them, at no extra cost to you.
- ## Star History
- [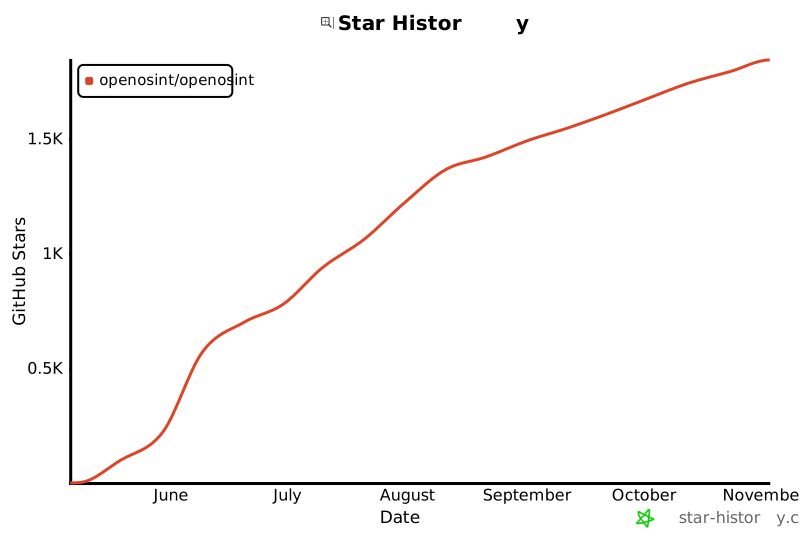](https://star-history.com/#OpenOSINT/OpenOSINT&Date)
openosint/tools/search_paste.py · Bundled script · 104 lines · 2 findings marked
- # openosint/tools/search_paste.py
- """
- Pastebin dump search module.
- Queries the psbdmp.ws public API to find pastes mentioning a target email
- address or username. Returns a formatted string; never raises on failure.
- """
- from __future__ import annotations
- import asyncio
- import logging
- import requests
- from openosint.proxy import get_requests_proxies
- from openosint.tools.exceptions import OSINTError, ToolExecutionError
- logger = logging.getLogger(__name__)
- _PSBDMP_URL = "https://psbdmp.ws/api/search/{query}"
- _DEFAULT_TIMEOUT = 15
- _MAX_RESULTS = 10
- def _fetch_paste_data(query: str, timeout_seconds: int) -> list[dict]:
- """
- Query psbdmp.ws for pastes mentioning query.
- Raises
- ------
- OSINTError
- On network failures.
- ToolExecutionError
- On unexpected HTTP status codes.
- """
- try:
- response = requests.get(
- _PSBDMP_URL.format(query=query),
- timeout=timeout_seconds,
- proxies=get_requests_proxies(),
- )
- except requests.RequestException as exc:
- raise OSINTError(f"Network error querying psbdmp.ws: {exc}") from exc
- if response.status_code == 404:
- return []
- if response.status_code != 200:
- raise ToolExecutionError(f"psbdmp.ws returned HTTP {response.status_code}.")
- data = response.json()
- return data.get("data", []) if isinstance(data, dict) else []
- def _format_paste_results(pastes: list[dict], query: str) -> str:
- """Return a structured string describing paste search findings."""
- if not pastes:
- return f"No pastes found mentioning '{query}'."
- count = len(pastes)
- shown = pastes[:_MAX_RESULTS]
- lines = [f"Found in {count} paste(s) for '{query}':\n"]
- for paste in shown:
- paste_id = paste.get("id", "unknown")
- date = paste.get("time", "unknown date")
- lines.append(f"[+] https://pastebin.com/{paste_id} ({date})")
- Dismissed after review: Quoted as data in code: Links to a paste site (pastebin.com), a common place to stage installer commands or send stolen data
- Dismissed after review: Talks to a raw IP address or throwaway host, where malware is often staged
- Line 66 on GitHub
- if count > _MAX_RESULTS:
- lines.append(f"\n... and {count - _MAX_RESULTS} more.")
- return "\n".join(lines)
- async def run_paste_osint(
- query: str,
- timeout_seconds: int = _DEFAULT_TIMEOUT,
- ) -> str:
- """
- Search Pastebin dumps for query via psbdmp.ws.
- Returns a descriptive error string on failure rather than raising.
- Parameters
- ----------
- query:
- Email address or username to search for.
- timeout_seconds:
- HTTP request timeout in seconds.
- Returns
- -------
- str
- Formatted result string or a descriptive error message.
- """
- logger.info("Starting paste search for: %s", query)
- try:
- pastes = await asyncio.to_thread(_fetch_paste_data, query, timeout_seconds)
- result = _format_paste_results(pastes, query)
- logger.info("Paste search complete for: %s", query)
- return result
- except OSINTError as exc:
- logger.warning("Paste search failed: %s", exc)
- return f"Scan error: {exc}"
- except Exception as exc:
- logger.exception("Unexpected error during paste search.")
- return f"Internal error: {exc}"
openosint/web/static/entity-graph.js · Bundled script · 608 lines · 2 findings marked
- /**
- * entity-graph.js — Entity normalizer registry.
- * Pure data in, pure data out. No DOM, no rendering.
- *
- * Node: { id, type, label, data }
- * id = "${type}:${value.toLowerCase()}" — stable dedupe key
- * data.isRoot = true marks the target node (visual hint only, not a separate namespace)
- *
- * Edge: { source, target, label }
- *
- * Entity types: email, username, domain, subdomain, ip, phone,
- * org, social_account, breach, paste, asn
- *
- * Every extractor is wrapped in try/catch; any parse failure degrades
- * gracefully to a generic target-linked node (never throws).
- */
- // ---------------------------------------------------------------------------
- // Target-type inference
- // ---------------------------------------------------------------------------
- const _IPv4_RE = /^(\d{1,3}\.){3}\d{1,3}$/;
- const _IPv6_RE = /^[0-9a-f:]{4,}$/i;
- const _DOMAIN_RE = /^[a-z0-9][a-z0-9\-._]*\.[a-z]{2,}$/i;
- const _PHONE_RE = /^\+?\d[\d\s\-().]{6,}$/;
- function _inferType(value) {
- const v = (value || '').trim();
- if (v.includes('@')) return 'email';
- if (_IPv4_RE.test(v)) return 'ip';
- if (_IPv6_RE.test(v) && v.includes(':')) return 'ip';
- if (_PHONE_RE.test(v) && !v.includes('.')) return 'phone';
- if (_DOMAIN_RE.test(v)) return 'domain';
- return 'username';
- }
- // ---------------------------------------------------------------------------
- // Node / edge constructors
- // ---------------------------------------------------------------------------
- function _node(type, value, data = {}) {
- const v = String(value).trim();
- return { id: `${type}:${v.toLowerCase()}`, type, label: v, data };
- }
- function _edge(sourceId, targetId, label) {
- return { source: sourceId, target: targetId, label };
- }
- // ---------------------------------------------------------------------------
- // Text parsing helpers
- // ---------------------------------------------------------------------------
- /** Extract the first value matching a prefixed line, e.g. "[+] Org: Google". */
- function _val(text, prefixPattern) {
- const re = new RegExp(`${prefixPattern}\\s*(.+)$`, 'm');
- const m = re.exec(text);
- return m ? m[1].trim() : null;
- }
- /** Extract ALL values matching a prefixed line. */
- function _vals(text, prefixPattern) {
- const re = new RegExp(`${prefixPattern}\\s*(.+)$`, 'gm');
- const results = [];
- let m;
- while ((m = re.exec(text)) !== null) results.push(m[1].trim());
- return results;
- }
- // ---------------------------------------------------------------------------
- // Normalizer registry — one entry per tool
- // Verbatim output samples are reproduced in tests/test_entity_graph.mjs.
- // ---------------------------------------------------------------------------
- const _REGISTRY = {
- /** search_ip output example:
- * IP intelligence for '8.8.8.8':
- * [+] Ip: 8.8.8.8
- * [+] Hostname: dns.google
- * [+] Org: AS15169 Google LLC
- * [+] City: Mountain View
- * [+] Country: US
- */
- search_ip(target, output) {
- const nodes = [], edges = [];
- const rootId = `ip:${target.toLowerCase().trim()}`;
- const org = _val(output, '\\[\\+\\] Org:');
- const hostname = _val(output, '\\[\\+\\] Hostname:');
- if (org) {
- const n = _node('org', org, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hosted by'));
- }
- if (hostname) {
- const n = _node('domain', hostname, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hostname'));
- }
- return { nodes, edges };
- },
- /** search_whois output example:
- * WHOIS results for 'example.com':
- * [+] Domain: EXAMPLE.COM
- * [+] Registrar: RESERVED-Internet Assigned Numbers Authority
- * [+] Emails: abuse@iana.org
- * [+] Org: Internet Assigned Numbers Authority
- * [+] Name Servers: a.iana-servers.net, b.iana-servers.net
- */
- search_whois(target, output) {
- const nodes = [], edges = [];
- const rootId = `domain:${target.toLowerCase().trim()}`;
- const registrar = _val(output, '\\[\\+\\] Registrar:');
- const org = _val(output, '\\[\\+\\] Org:');
- const emailRaw = _val(output, '\\[\\+\\] Emails:');
- const nsRaw = _val(output, '\\[\\+\\] Name Servers:');
- if (registrar) {
- const n = _node('org', registrar, { role: 'registrar' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'registered by'));
- }
- if (org) {
- const n = _node('org', org, { role: 'registrant' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'owned by'));
- }
- if (emailRaw) {
- emailRaw.split(',').forEach(e => {
- const em = e.trim();
- if (em.includes('@')) {
- const n = _node('email', em, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'contact'));
- }
- });
- }
- if (nsRaw) {
- nsRaw.split(',').forEach(ns => {
- const d = ns.trim();
- if (d) {
- const n = _node('domain', d, { role: 'nameserver' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'ns'));
- }
- });
- }
- return { nodes, edges };
- },
- /** search_breach output example:
- * Found in 2 breach(es) for 'test@example.com':
- * [+] Adobe (2013-10-04) — leaked: Email addresses, Passwords, Usernames
- * [+] LinkedIn (2012-05-05) — leaked: Email addresses, Passwords
- */
- search_breach(target, output) {
- const nodes = [], edges = [];
- const rootId = `email:${target.toLowerCase().trim()}`;
- const re = /^\[\+\] ([^\s(]+)\s*\(([^)]+)\)/gm;
- let m;
- while ((m = re.exec(output)) !== null) {
- const n = _node('breach', m[1], { date: m[2] });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'breached in'));
- }
- return { nodes, edges };
- },
- /** search_dns output example:
- * [DNS] Domain: example.com
- * [DNS] A: 93.184.216.34
- * [DNS] MX records:
- * • 0 mail.example.com.
- * [DNS] NS: a.iana-servers.net, b.iana-servers.net
- */
- search_dns(target, output) {
- const nodes = [], edges = [];
- const rootId = `domain:${target.toLowerCase().trim()}`;
- const aRaw = _val(output, '\\[DNS\\] A:');
- if (aRaw) {
- aRaw.split(/[,\s]+/).forEach(ip => {
- ip = ip.trim();
- if (_IPv4_RE.test(ip)) {
- const n = _node('ip', ip, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'resolves to'));
- }
- });
- }
- const lines = output.split('\n');
- let inMx = false;
- for (const line of lines) {
- if (line.includes('[DNS] MX records:')) { inMx = true; continue; }
- if (/^\[DNS\]/.test(line) || /^\[!]/.test(line)) {
- if (line.includes('[DNS] NS:')) {
- const nsRaw = line.replace(/.*\[DNS\] NS:/, '').trim();
- nsRaw.split(',').forEach(ns => {
- const d = ns.trim().replace(/\.$/, '');
- if (d) {
- const n = _node('domain', d, { role: 'ns' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'ns'));
- }
- });
- }
- inMx = false;
- continue;
- }
- if (inMx && line.trim().startsWith('•')) {
- const host = line.replace('•', '').trim().split(/\s+/).pop()?.replace(/\.$/, '');
- if (host && _DOMAIN_RE.test(host)) {
- const n = _node('domain', host, { role: 'mx' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'mail server'));
- }
- }
- }
- return { nodes, edges };
- },
- /** search_ip2location output example:
- * [IP2Location] IP: 8.8.8.8
- * [IP2Location] ISP: Google LLC
- * [IP2Location] Domain: google.com
- * [IP2Location] ASN: AS15169
- */
- search_ip2location(target, output) {
- const nodes = [], edges = [];
- const rootId = `ip:${target.toLowerCase().trim()}`;
- const isp = _val(output, '\\[IP2Location\\] ISP:');
- const asn = _val(output, '\\[IP2Location\\] ASN:');
- const domain = _val(output, '\\[IP2Location\\] Domain:');
- if (isp && isp !== 'N/A') {
- const n = _node('org', isp, { role: 'isp' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hosted by'));
- }
- if (asn && asn !== 'N/A') {
- const n = _node('asn', asn, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'belongs to'));
- }
- if (domain && domain !== 'N/A') {
- const n = _node('domain', domain, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'reverse domain'));
- }
- return { nodes, edges };
- },
- /** search_abuseipdb output example:
- * [AbuseIPDB] IP: 8.8.8.8
- * [AbuseIPDB] Abuse Confidence Score: 0%
- * [AbuseIPDB] ISP: Google LLC
- * [AbuseIPDB] Domain: google.com
- * [AbuseIPDB] Country: US
- */
- search_abuseipdb(target, output) {
- const nodes = [], edges = [];
- const rootId = `ip:${target.toLowerCase().trim()}`;
- const isp = _val(output, '\\[AbuseIPDB\\] ISP:');
- const domain = _val(output, '\\[AbuseIPDB\\] Domain:');
- const score = _val(output, '\\[AbuseIPDB\\] Abuse Confidence Score:');
- if (isp && isp !== 'N/A') {
- const n = _node('org', isp, { role: 'isp' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hosted by'));
- }
- if (domain && domain !== 'N/A') {
- const n = _node('domain', domain, { abuseScore: score });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'reverse domain'));
- }
- return { nodes, edges };
- },
- /** search_shodan (host) output example:
- * Shodan host data for '8.8.8.8':
- * [+] IP: 8.8.8.8
- * [+] Org: Google LLC
- * [+] Hostnames: dns.google, 8888.google
- * [+] Open ports: 53, 443
- *
- * search_shodan (search) output example:
- * Shodan search results for 'nginx' (1000 total, showing 3):
- * [+] 1.2.3.4:80 — Acme Corp — United States
- */
- search_shodan(target, output) {
- const nodes = [], edges = [];
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${target.toLowerCase().trim()}`;
- const org = _val(output, '\\[\\+\\] Org:');
- if (org) {
- const n = _node('org', org, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hosted by'));
- }
- const hostsRaw = _val(output, '\\[\\+\\] Hostnames:');
- if (hostsRaw) {
- hostsRaw.split(',').forEach(h => {
- h = h.trim();
- if (h) {
- const n = _node('domain', h, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'hostname'));
- }
- });
- }
- // Search-result bullets: "[+] 1.2.3.4:80 — Org — Country"
- const searchRe = /^\[\+\] ([\d.]+):\d+ — (.+?) — .+$/gm;
- let m;
- while ((m = searchRe.exec(output)) !== null) {
- const ipNode = _node('ip', m[1], {});
- nodes.push(ipNode); edges.push(_edge(rootId, ipNode.id, 'found'));
- const orgName = m[2];
- if (orgName && orgName !== 'unknown') {
- const orgNode = _node('org', orgName, {});
- nodes.push(orgNode); edges.push(_edge(ipNode.id, orgNode.id, 'hosted by'));
- }
- }
- return { nodes, edges };
- },
- /** search_virustotal output example:
- * [VirusTotal] Malicious: 2
- * [VirusTotal] ASN: AS15169 Google LLC
- * [VirusTotal] Country: US
- * [VirusTotal] Registrar: MarkMonitor Inc.
- */
- search_virustotal(target, output) {
- const nodes = [], edges = [];
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${target.toLowerCase().trim()}`;
- const asn = _val(output, '\\[VirusTotal\\] ASN:');
- const registrar = _val(output, '\\[VirusTotal\\] Registrar:');
- if (asn) {
- const n = _node('asn', asn, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'belongs to'));
- }
- if (registrar) {
- const n = _node('org', registrar, { role: 'registrar' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'registered by'));
- }
- return { nodes, edges };
- },
- /** search_github output example (direct profile):
- * [GitHub] Login: octocat
- * [GitHub] Name: The Octocat
- * [GitHub] Company: GitHub
- * [GitHub] Email (profile): N/A
- * [GitHub] Profile URL: https://github.com/octocat
- * [GitHub] Emails found in commits: octocat@github.com
- *
- * search_github output example (search results):
- * [GitHub] Search results for 'johndoe' (2 match(es)):
- * • johndoe — https://github.com/johndoe (type: User)
- */
- search_github(target, output) {
- const nodes = [], edges = [];
- const login = _val(output, '\\[GitHub\\] Login:');
- const rootId = `username:${(login || target).toLowerCase().trim()}`;
- const email = _val(output, '\\[GitHub\\] Email \\(profile\\):');
- const company = _val(output, '\\[GitHub\\] Company:');
- const profileUrl = _val(output, '\\[GitHub\\] Profile URL:');
- const commitEmails = _val(output, '\\[GitHub\\] Emails found in commits:');
- if (profileUrl) {
- const n = _node('social_account', profileUrl, { platform: 'github', login: login || target });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found on'));
- }
- if (email && email !== 'N/A') {
- const n = _node('email', email, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'email'));
- }
- if (company && company !== 'N/A') {
- const n = _node('org', company, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'works at'));
- }
- if (commitEmails) {
- commitEmails.split(',').forEach(e => {
- const em = e.trim();
- if (em.includes('@')) {
- const n = _node('email', em, { source: 'commit' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'commit email'));
- }
- });
- }
- // Search-result bullets: " • johndoe — https://github.com/johndoe (type: User)"
- const searchRe = /•\s+(\S+)\s+—\s+(https?:\/\/\S+)/gm;
- let m;
- while ((m = searchRe.exec(output)) !== null) {
- const n = _node('social_account', m[2], { platform: 'github', login: m[1] });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found on'));
- }
- return { nodes, edges };
- },
- /** search_censys output example (IP):
- * [Censys] Type: ip
- * [Censys] IP: 8.8.8.8
- * [Censys] ASN: AS15169 GOOGLE
- * [Censys] Country: US
- *
- * search_censys output example (domain/cert):
- * [Censys] Domain: example.com
- * [Censys] Certificates Found: 3
- * [Censys] SANs: example.com, www.example.com, api.example.com
- */
- search_censys(target, output) {
- const nodes = [], edges = [];
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${target.toLowerCase().trim()}`;
- const ip = _val(output, '\\[Censys\\] IP:');
- const asn = _val(output, '\\[Censys\\] ASN:');
- const sansRaw = _val(output, '\\[Censys\\] SANs:');
- if (ip && ip.toLowerCase() !== target.toLowerCase().trim()) {
- const n = _node('ip', ip, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'resolves to'));
- }
- if (asn) {
- const n = _node('asn', asn, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'belongs to'));
- }
- if (sansRaw) {
- sansRaw.split(',').forEach(d => {
- d = d.trim();
- if (d && d.toLowerCase() !== target.toLowerCase().trim()) {
- const n = _node('domain', d, { role: 'san' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'certificate san'));
- }
- });
- }
- return { nodes, edges };
- },
- /** search_paste output example:
- * Found in 2 paste(s) for 'test@example.com':
- * [+] https://pastebin.com/abc12345 (2023-01-15)
- Note: Quoted as data in code: Links to a paste site (pastebin.com), a common place to stage installer commands or send stolen data
- Line 439 on GitHub
- * [+] https://pastebin.com/xyz98765 (2022-08-03)
- Note: Quoted as data in code: Links to a paste site (pastebin.com), a common place to stage installer commands or send stolen data
- Line 440 on GitHub
- */
- search_paste(target, output) {
- const nodes = [], edges = [];
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${target.toLowerCase().trim()}`;
- const re = /^\[\+\] (https?:\/\/\S+)\s*\(([^)]+)\)/gm;
- let m;
- while ((m = re.exec(output)) !== null) {
- const n = _node('paste', m[1], { date: m[2] });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found in'));
- }
- return { nodes, edges };
- },
- /** search_footprint output example:
- * [Footprint] URL: https://twitter.com/johndoe
- * [Footprint] Domain: twitter.com
- * [Footprint] URL: https://linkedin.com/in/johndoe
- * [Footprint] Domain: linkedin.com
- */
- search_footprint(target, output) {
- const nodes = [], edges = [];
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${target.toLowerCase().trim()}`;
- _vals(output, '\\[Footprint\\] URL:').forEach(url => {
- const n = _node('social_account', url, { source: 'footprint' });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'links to'));
- });
- _vals(output, '\\[Footprint\\] Domain:').forEach(d => {
- const n = _node('domain', d, {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found at'));
- });
- return { nodes, edges };
- },
- // ---- Type-B demo stubs (verbatim patterns from agent-loop.js _TYPE_B_DEMO) ----
- /** search_email Type-B demo stub:
- * [DEMO DATA — install holehe: pip install holehe]
- * [+] github.com — demo@example.com registered (sample)
- * [+] spotify.com — demo@example.com registered (sample)
- * [-] twitter.com — not found (sample)
- */
- search_email(target, output) {
- const nodes = [], edges = [];
- const rootId = `email:${target.toLowerCase().trim()}`;
- const re = /^\[\+\] (\S+)\s+—\s+\S+\s+registered/gm;
- let m;
- while ((m = re.exec(output)) !== null) {
- const n = _node('social_account', m[1], { platform: m[1] });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found on'));
- }
- return { nodes, edges };
- },
- /** search_username Type-B demo stub:
- * [DEMO DATA — install sherlock: pip install sherlock-project]
- * [+] GitHub https://github.com/demouser (sample)
- * [+] Reddit https://reddit.com/u/demouser (sample)
- * [-] Instagram not found (sample)
- */
- search_username(target, output) {
- const nodes = [], edges = [];
- const rootId = `username:${target.toLowerCase().trim()}`;
- const re = /^\[\+\] (\S+)\s+(https?:\/\/\S+)\s+\(sample\)/gm;
- let m;
- while ((m = re.exec(output)) !== null) {
- const n = _node('social_account', m[2], { platform: m[1] });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'found on'));
- }
- return { nodes, edges };
- },
- /** search_domain Type-B demo stub:
- * [DEMO DATA — install sublist3r: pip install sublist3r]
- * [+] www.example.com (sample subdomain)
- * [+] mail.example.com (sample subdomain)
- * [+] api.example.com (sample subdomain)
- */
- search_domain(target, output) {
- const nodes = [], edges = [];
- const rootId = `domain:${target.toLowerCase().trim()}`;
- const re = /^\[\+\] (\S+)\s+\(sample subdomain\)/gm;
- let m;
- while ((m = re.exec(output)) !== null) {
- const n = _node('subdomain', m[1], {});
- nodes.push(n); edges.push(_edge(rootId, n.id, 'subdomain'));
- }
- return { nodes, edges };
- },
- /** search_phone Type-B demo stub:
- * [DEMO DATA — install phoneinfoga: github.com/sundowndev/phoneinfoga/releases]
- * [+] Number: +14155550100 (sample)
- * [+] Country: US
- * [+] Carrier: Sample Carrier LLC (sample)
- * [+] Line type: mobile (sample)
- */
- search_phone(target, output) {
- const nodes = [], edges = [];
- const rootId = `phone:${target.toLowerCase().trim()}`;
- const carrier = _val(output, '\\[\\+\\] Carrier:');
- const country = _val(output, '\\[\\+\\] Country:');
- if (carrier) {
- const carrierClean = carrier.replace(/\s*\(sample\)\s*$/, '').trim();
- const n = _node('org', carrierClean, { role: 'carrier', country });
- nodes.push(n); edges.push(_edge(rootId, n.id, 'carrier'));
- }
- return { nodes, edges };
- },
- // Informational / dork tools produce no meaningful graph nodes
- generate_dorks() { return { nodes: [], edges: [] }; },
- search_dorks_live() { return { nodes: [], edges: [] }; },
- scrape_url() { return { nodes: [], edges: [] }; },
- };
- // ---------------------------------------------------------------------------
- // Public API
- // ---------------------------------------------------------------------------
- export function inferEntityType(value) {
- return _inferType(value);
- }
- /**
- * Build the root target node with the same id scheme as normalizers use,
- * so tools that rediscover the same entity merge into one node.
- * data.isRoot = true marks it visually — NOT a separate id namespace.
- */
- export function makeTargetNode(target) {
- const v = (target || '').trim();
- const type = _inferType(v);
- return {
- id: `${type}:${v.toLowerCase()}`,
- type,
- label: v,
- data: { isRoot: true },
- };
- }
- /**
- * Extract graph nodes and edges from a tool result.
- * Never throws — any parse failure returns a single generic node linked to the target.
- */
- export function extractEntities(toolName, target, output) {
- const inferredType = _inferType(target);
- const rootId = `${inferredType}:${(target || '').toLowerCase().trim()}`;
- const extractor = _REGISTRY[toolName];
- if (!extractor) {
- const n = _node('social_account', `${toolName}:${target}`, { tool: toolName });
- return { nodes: [n], edges: [_edge(rootId, n.id, 'found by ' + toolName)] };
- }
- try {
- const result = extractor(target, output || '');
- return {
- nodes: Array.isArray(result?.nodes) ? result.nodes : [],
- edges: Array.isArray(result?.edges) ? result.edges : [],
- };
- } catch {
- const n = _node('social_account', `${toolName}:${target}:error`, { tool: toolName, parseError: true });
- return { nodes: [n], edges: [_edge(rootId, n.id, 'found by ' + toolName)] };
- }
- }
Ratings and comments
Sign in to rate this skill.
Sign inFree to use. If it’s helped, pass it on.